Security improvement - training
Thinking Like an Attacker
Cocoon teaches security professionals to assess physical security holistically from the perspective of an adversary.
- Two-day on-site training, from mindset to practice and from practice to advisory
- Conduct a Physical Security Assessment yourself under the guidance of Red Team specialists
- Translating findings into persuasive advice for management
Thinking Like an Attacker training at Cocoon
Thinking Like an Attacker is a two-day on-site training course in which security professionals learn to think like an attacker. Not from a compliance or technical standpoint, but from the question of how an adversary would actually approach an object.
The training builds from mindset to practice to advisory. Day one covers the methods and modus operandi of professional attackers, the principle of Security in Depth, and the role of state actors. Day two translates this directly into practice: under the guidance of experienced Red Team specialists, participants conduct a Physical Security Assessment at their own location and learn to convert the findings into a clear assessment report and persuasive advice for management.
Participants develop a bird’s-eye view that allows them to recognize vulnerabilities before an adversary discovers them. They learn to see through the entire security chain—organizational, structural, electronic, and human—and to recognize the connections between small vulnerabilities that an attacker specifically looks for. Additionally, they build the ability to translate technical findings into risk-driven advice that actually prompts executives to take action.
Who is this training intended for?
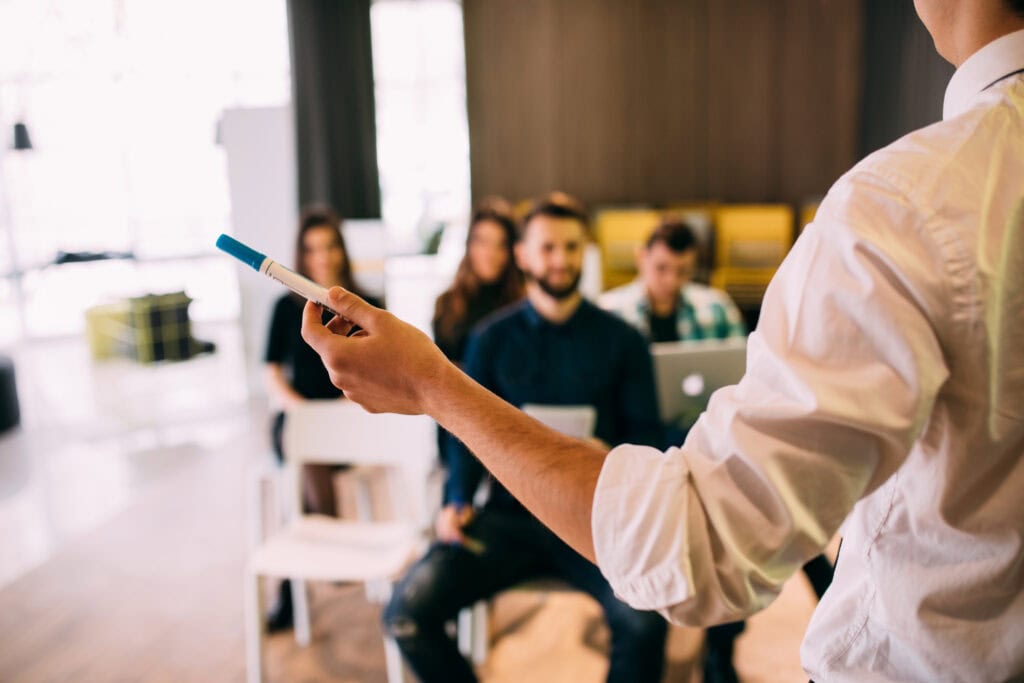
The training is intended for security professionals and internal security specialists responsible for assessing, designing, or advising on physical security measures, particularly at organizations with high security requirements such as high-tech industry, critical infrastructure, and financial institutions.
This is a different level than the other training courses in the Cocoon portfolio: while courses such as Predictive Profiling and Aggression Reduction & Communication focus on frontline staff, Thinking Like an Attacker is intended for the professionals who determine the security strategy themselves, implement it, or advise management on it.
Why choose Cocoon
Cocoon does not just let participants think like an attacker, but also apply that thinking immediately: day two takes place at your own location, under the guidance of experienced Red Team specialists who apply this approach daily in practice. That makes the difference between a theoretical framework and an assessment report that the organization can actually use.
Compliance does not automatically mean resilience.
Thinking Like an Attacker combines well with a physical penetration test or Red Teaming: the training provides security professionals with the frame of reference to interpret findings from such a test themselves and translate them into policy.
- Guidance by experienced Red Team specialists, not just theorists
- Day two takes place at your own location, resulting in a real assessment report
- Focused on persuading executives, not just on technical knowledge
Cocoon works for renowned (publicly) listed companies in profit and non-profit environments; references are available upon request.
Frequently asked questions
What is the Cost of the Attacker’s Mindset Training?
The costs depend on the group size and the preparation required for the on-site assessment on day two. After a brief intake, you will receive a customized quote.
How Long Does the Attacker Mindset Training Last?
Two days. Day one addresses the mindset and methods of attackers; day two directly applies this to a Physical Security Assessment at your site.
Is there a certificate associated with the training?
Cocoon’s training primarily focuses on practical application within your own organization, not on external certification.
What is the difference between this training and a physical penetration test or Red Teaming?
In a physical penetration test or Red Teaming, Cocoon performs the test itself. With Thinking Like an Attacker, your own security professionals learn that perspective and assessment method, ensuring your organization possesses that internal capability independently of a specific test.
Who is this training for?
For security professionals and internal security specialists responsible for assessing, implementing, or advising on physical security measures, particularly within organizations with high security requirements.
Do participants actually conduct an assessment themselves at our own location?
Yes. On day two, under the guidance of experienced Red Team specialists, participants conduct a Physical Security Assessment at their own location, including an assessment report and management recommendations.