Practical Validation - Controlled Testing
Red Teaming
Cocoon deploys a team of specialists to test, from an offensive position, whether your physical security, processes, and personnel can effectively stop a serious adversary.
- Realistic attack simulation on buildings, grounds, and processes, executed within pre-defined frameworks
- Available in two forms, white box and black box, tailored to your threat profile
- Reporting with concrete, priority-oriented improvement measures
What is Red Teaming?
Red Teaming is a realistic attack simulation in which Cocoon acts as a serious adversary to test whether an organization’s physical security, procedures, and employees hold up in practice. A team of specialists attempts to reach specific assets to be protected from an offensive position, within pre-agreed frameworks.
The service is intended for organizations with critical processes, high-risk environments, or sensitive information, such as industry, critical infrastructure, and organizations with OT environments. Cocoon performs Red Teaming from a physical perspective, not as a cyber-attack simulation, and utilizes it when an organization wants to know if its security also stands up against a determined, well-prepared adversary.
How Red Teaming Works at Cocoon
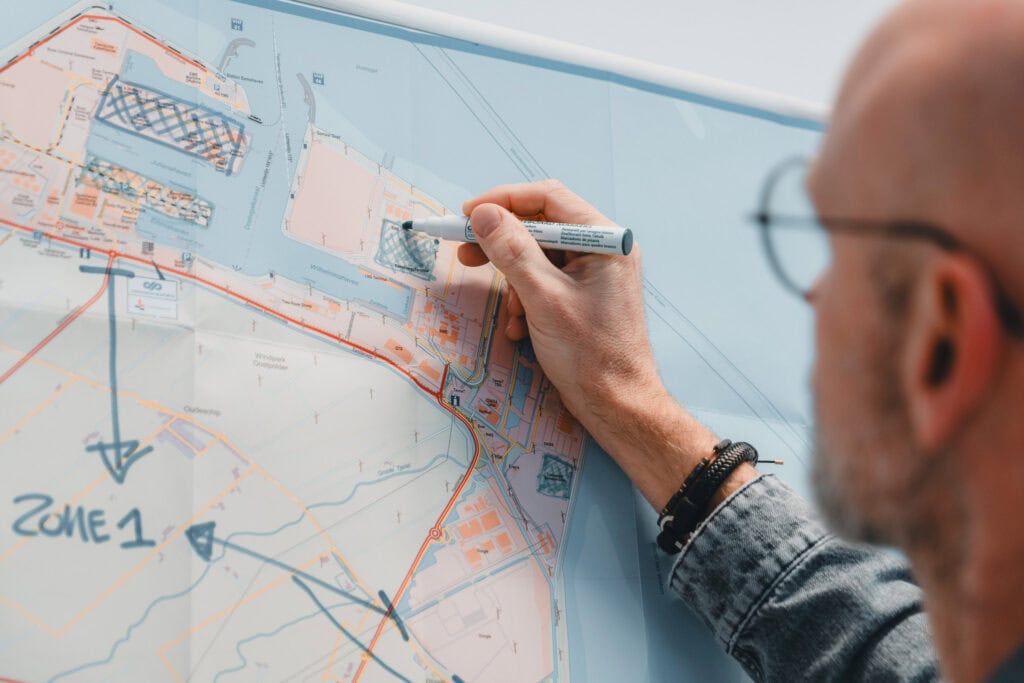
In many alternatives, Red Teaming is primarily used as a cyber exercise, with physical access as an afterthought. Cocoon reverses that: physical intrusion, human behavior, and procedures are central, supplemented where relevant with other attack paths. This creates a realistic picture of how an adversary would actually approach your organization.
Cocoon works in four fixed phases.
Cocoon offers Red Teaming at two levels, depending on how much prior knowledge your organization shares in advance.
With white box Red Teaming, you share information in advance about systems, protocols, and assets to be protected. A team of several specialists from various disciplines works from an offensive position within that clearly defined scope. This form is targeted and controlled, and suitable when you want to have specific zones, systems, or scenarios tested. You receive a comprehensive report with a dashboard and, in the case of acute vulnerabilities, an immediate interim notification if desired.
With black box Red Teaming, our team receives no or minimal information in advance, similar to an attacker who does not know your organization from the inside. This requires more extensive preparation, including our own observation and research, and may involve the deployment of multiple teams simultaneously. Interim evaluation moments keep the process controlled, even though the approach is less predictable. This is the most realistic form of Red Teaming and the best indicator of how your organization holds up against an unknown adversary.
Regardless of the chosen form, execution is followed by a debriefing with those involved. This provides immediate insight into what happened and why, even before the full report is available. Finally, you will receive a comprehensive report with findings, evidence, and concrete, priority-oriented improvement measures.
Why choose Cocoon
For Cocoon, Red Teaming is the most comprehensive instrument within a broader improvement process: it shows how your organization holds up when multiple layers of security are under pressure simultaneously. We do not assess security measures we have provided ourselves, which makes our findings objective. Our team combines specialists from various disciplines with years of experience in high-risk environments.
- Experience with high-risk scenarios and critical infrastructure
- Multidisciplinary team, assembled per assignment
- Two forms, white box and black box, tailored to your threat profile
Please note: under NIS2 and the General Security Requirements for Central Government Commissions (ABRO), actual testing of security measures is required.
Red Teaming helps with the requirements of NIS 2 and the ABRO.
Cocoon works for renowned (publicly) listed companies in profit and non-profit environments; references are available upon request.
Frequently asked questions
How Much Does Red Teaming Cost?
The cost of Red Teaming is estimated per engagement and depends on the scope, the number of specialists, and the chosen approach, white box or black box. After the intake, you will receive a customized quote, tailored to your threat profile and the assets to be protected.
How Long Does a Red Teaming Engagement Last?
A Red Teaming engagement typically lasts several weeks to months, depending on the chosen approach. A black box engagement requires more preparation time than a white box, as our team must first gather information independently.
Is Red Teaming Legal?
Yes. Red Teaming is conducted solely with the client’s written consent, within pre-established Rules of Engagement and guidelines. These frameworks ensure the engagement proceeds lawfully and in a controlled manner.
What is the difference between white box and black box Red Teaming?
With white box Red Teaming, you share information about systems and protocols in advance, allowing for a more targeted test. With black box Red Teaming, our team receives little to no information beforehand, similar to an attacker who does not know your organization from the inside. This requires more preparation time but provides the most realistic simulation.
What is the difference between Red Teaming and a physical penetration test?
A physical penetration test focuses on specific components of your security, conducted by a single auditor or a small team. Red Teaming is broader: multiple specialists operate from an offensive position along several attack paths simultaneously, aimed at actually reaching specific assets to be protected.
Does Red Teaming Disrupt Daily Operations?
No. Red Teaming also adheres to pre-established rules that prevent disruption to your organization and limit the permissible impact. Cocoon operates in a controlled and proportionate manner, regardless of the chosen approach.
Is Red Teaming the same as cyber red teaming?
Not necessarily. Many organizations primarily utilize red teaming for cyberattack simulations. Cocoon conducts physical Red Teaming: our specialists operate from an offensive position against buildings, premises, and processes, not primarily against IT systems.