Practical Validation - Controlled Testing
Physical Penetration Test
Cocoon tests whether your security measures, procedures, and employees actually stop an unauthorized act.
- Realistic physical access attempts, executed within pre-agreed frameworks
- Available as a basic or standard test, matching the desired scope
- Reporting with concrete, immediately applicable improvement measures
What is a physical penetration test,
also known as a physical pentest?
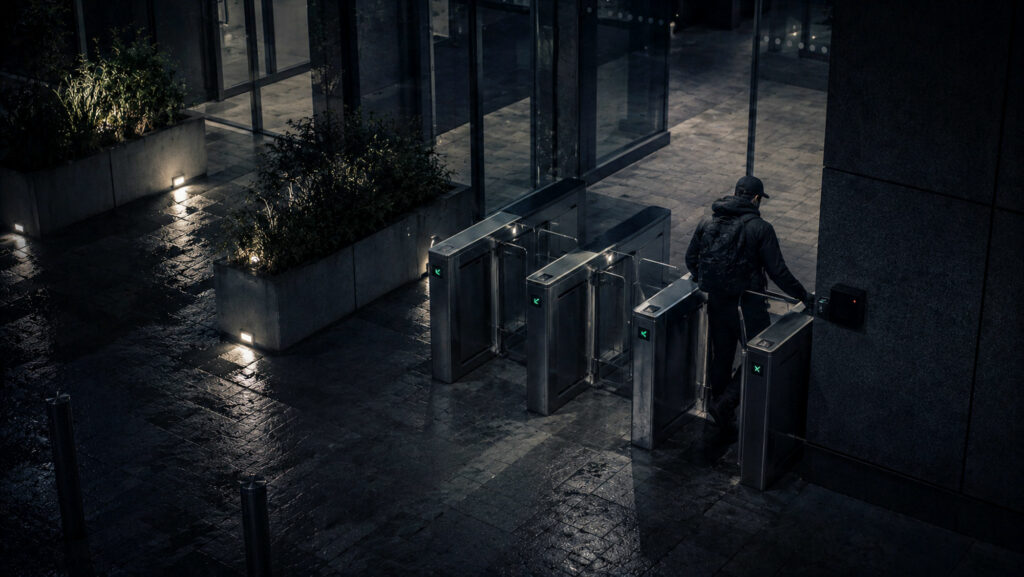
A physical penetration test is a practical assessment in which Cocoon, with the client’s permission, attempts to gain access to buildings, grounds, departments, or critical systems without valid authorization. The test measures whether security measures, procedures, and employee alertness actually work in practice, not just on paper.
The service is relevant for organizations with sensitive areas, critical processes, or valuable assets, such as server rooms, OT environments, and production sites. A physical penetration test is often deployed after an investment in security, following a relocation or renovation, during new processes, or as a periodic validation when doubt exists regarding the practical effectiveness of existing measures.
How Cocoon Conducts a Physical Penetration Test
With many alternatives, an assessment remains limited to a paper-based check or an exclusively technical look at locks and cameras. Realistic scenarios and the role of employees then remain underexposed, while that is precisely where most vulnerabilities arise. Compliance does not automatically mean resilience.
Cocoon works in four fixed phases.
Cocoon offers the physical penetration test in two forms, depending on the desired scope and depth.
In the basic variant, one auditor tests a defined part of your security, such as access control at the main entrance or the behavior of the reception desk during an unannounced visit. This form is targeted and compact, and suitable when you want to have a specific part of your security tested without immediately launching a broad investigation. You will receive a clear report with findings and a concrete direction for improvement.
In the standard variant, a team of two experts tests multiple components simultaneously, from key and badge management to tailgating and reception processes. This form provides a more complete picture of how your security holds up as a whole and is performed with additional tools such as cameras and lockpicking tools. You will receive a more extensive report with a priority-oriented direction for improvement.
Regardless of the chosen form, our team tests specific components of your security in a controlled and proportional manner, within the agreed frameworks. A debriefing with those involved follows immediately afterward. This gives you immediate insight into what happened and why, even before the report is ready, and reduces resistance because everyone experiences the process together.
Finally, you will receive a report with findings, evidence, and a concrete, priority-oriented direction for improvement. Not just what went wrong, but also why, and what that means for your organization’s resilience.
Why choose Cocoon
For Cocoon, a physical penetration test is not a one-time snapshot, but a deliberately chosen starting point: a baseline measurement and benchmark for your organization’s resilience. We do not assess security measures we have supplied ourselves, which makes our findings objective. Our team works multidisciplinarily, with knowledge of organizational, structural, electronic, and human security factors.
Not a vendor of individual tests, but your long-term partner in security awareness.
From that starting point, we continue to measure together in repeated improvement cycles, ensuring that measures do not fade into routine or a false sense of security.
- Independent validation, separate from provided security systems
- Basic and standard variants, matching the desired scope and depth
- A starting point for an ongoing improvement process, not a one-time test
Please note: under NIS2 and the General Security Requirements for Central Government Commissions (ABRO), actual testing of security measures is required.
Performing a physical penetration test helps meet the requirements of NIS 2 and the ABRO.
Cocoon works for renowned (publicly) listed companies in profit and non-profit environments; references are available upon request.
Frequently asked questions
How Much Does a Physical Penetration Test Cost?
The cost of a physical penetration test depends on the size of the location, the number of scenarios, and the complexity of the scope. Following the intake, you will receive a customized quote, tailored to your threat profile and assets to be protected.
What is the difference between a basic and a standard physical penetration test?
In the basic version, a single auditor tests a specific aspect of your security, such as access control or the conduct of your reception staff. In the standard version, a team of two experts tests multiple areas concurrently, using additional tools and providing a more comprehensive report. We determine the best fit together, based on your scope and threat profile.
How Long Does a Physical Penetration Test Take?
A physical penetration test typically lasts several weeks, from intake to reporting. A debriefing follows immediately after the assessment, so you don’t have to wait for the report to receive initial insights.
Is a physical penetration test legal?
Yes. A physical penetration test is performed exclusively with the written consent of the client, within pre-established Rules of Engagement. These frameworks ensure that the test is conducted lawfully and in a controlled manner.
What is the Difference Between a Physical Penetration Test and a Mystery Visit?
A Mystery Visit is conducted by a single tester, without tools, focusing on initial access and reception, and includes a brief report. A physical penetration test is more in-depth: depending on the scope, one auditor or a team of two experts will test multiple components of your security, utilizing tools and providing a more comprehensive report.
What is the Difference Between a Physical Penetration Test and Red Teaming?
A physical penetration test focuses on specific components of your physical security. Red Teaming takes a broader approach: multiple specialists operate from an offensive position across multiple attack vectors, targeting specific protected assets, with more extensive preparation and dashboard reporting.
Does a physical penetration test disrupt daily business operations?
No. The test is coordinated in advance within clear Rules of Engagement to ensure that the impact on your processes remains limited. Cocoon operates in a controlled and proportional manner, with clear agreements on what is and is not permitted.
What happens if employees accidentally grant access?
This is precisely what the test measures. The results are not used to penalize individual employees, but to specifically improve procedures, training, and security awareness.
What tools do you use for a physical penetration test?
Depending on the scenario and the security challenge, cameras, lockpicking tools, counterfeit security passes, and IDs are deployed. For more advanced standard variants and Red Teaming, technical means for manipulating security technology, drones, divers, and other specialists may also be utilized.